Logs Without Pipelines, Queries Without Servers
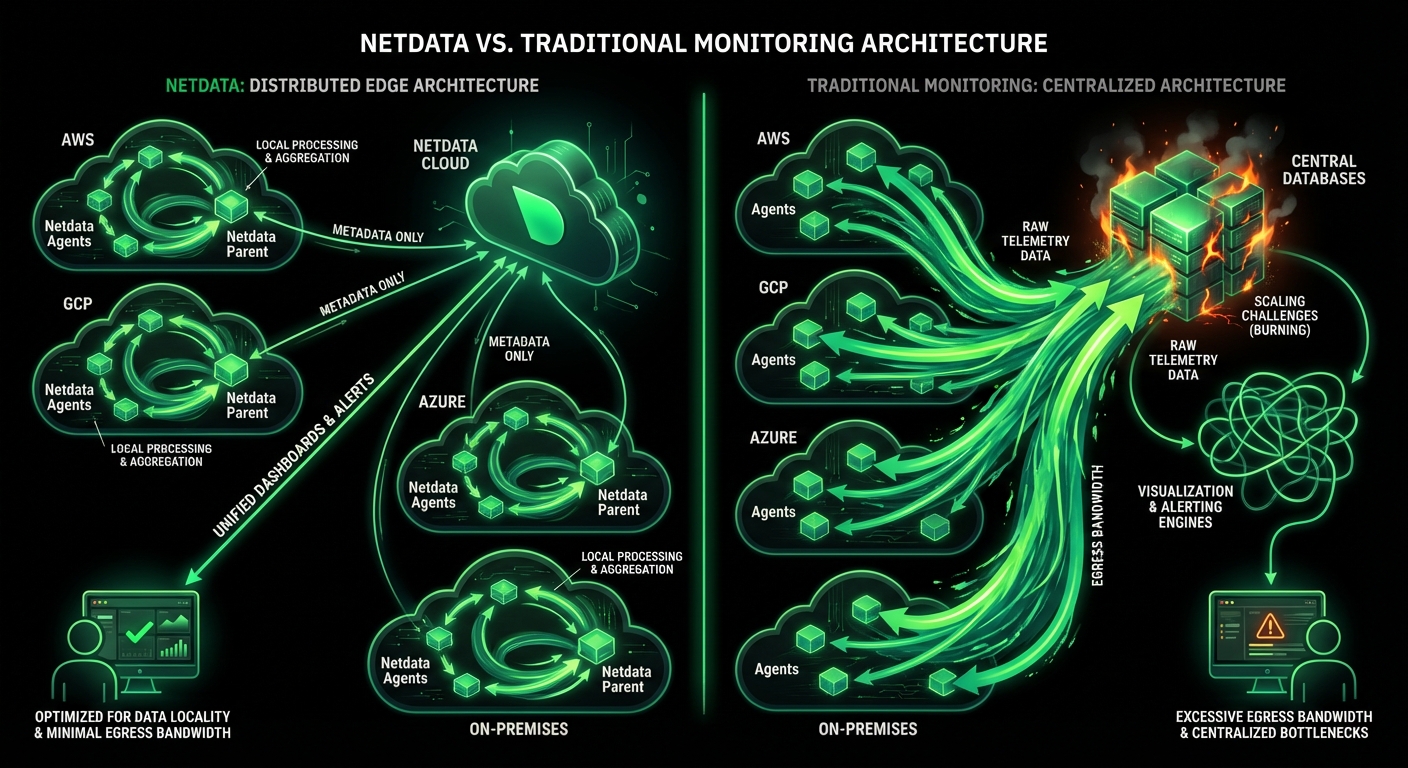
Log management should leverage native formats for efficient, comprehensive log analysis at the edge - eliminating expensive centralized pipelines and query servers.
Why This Matters: 90% cost reduction - eliminate Elasticsearch/Splunk infrastructure and storage multiplication; Logs Monitoring (querying logs in place) is not billed. No data loss - keep all logs without sampling or filtering to manage costs. 200× more accurate - analyzes 1M entries before sampling vs 5K for traditional tools. Instant correlation - logs and metrics from same source, no timestamp matching or separate systems. Compliance support - systemd-journal Forward Secure Sealing for journal tamper detection, data stays at edge for GDPR/sovereignty.
How We Deliver: Direct file access - clients open journal files directly, no query servers needed. Comprehensive indexing - every field in every log entry automatically indexed by journald. Flexible schema - each entry can have unique fields, all fully searchable. Native tooling - built-in centralization, filtering, exporting via systemd-journal-upload. Log transformation - log2journal converts text/JSON/logfmt into structured, indexed entries. Windows support - full Windows Event Logs, ETW, and TraceLogging, unified logging across platforms. Any other source - Logs Management collects files, syslog, Kubernetes, application and cloud logs through the OpenTelemetry Collector into Netdata’s log store, with every field indexed.
The Innovation: Instead of copying every log to expensive centralized systems, we built better tools on the robust foundation already present in every system, and centralize only the logs that need it in Netdata’s own log store - eliminating needless data movement while delivering superior capabilities.
90% Cost Savings
Learn About Zero-Pipeline Logs




 Our Core Philosophy